Cyber Attack Disables Commercial Freezers Across Seven European Countries, Causing Major Food Losses
Cyber Attack Disables Commercial Freezers Across Seven European Countries, Causing Major Food Losses
BRUSSELS — A suspected cyber attack targeting commercial refrigeration systems has disrupted supermarket operations across at least seven European countries, forcing retailers to dispose of large quantities of spoiled food and raising fresh concerns about vulnerabilities in internet-connected infrastructure.
The incidents, which reportedly affected supermarkets in Belgium, Luxembourg, Sweden, Ireland, Estonia, the Netherlands, and France, have drawn the attention of cybersecurity specialists and law enforcement agencies as they investigate how attackers gained access to refrigeration controls.
Retail operators say the disruptions resulted in significant financial losses, with refrigerated and frozen goods becoming unusable after cooling systems malfunctioned. The attacks have also highlighted the growing risks associated with the increasing use of connected devices throughout the retail sector.
Supermarkets Report Significant Losses
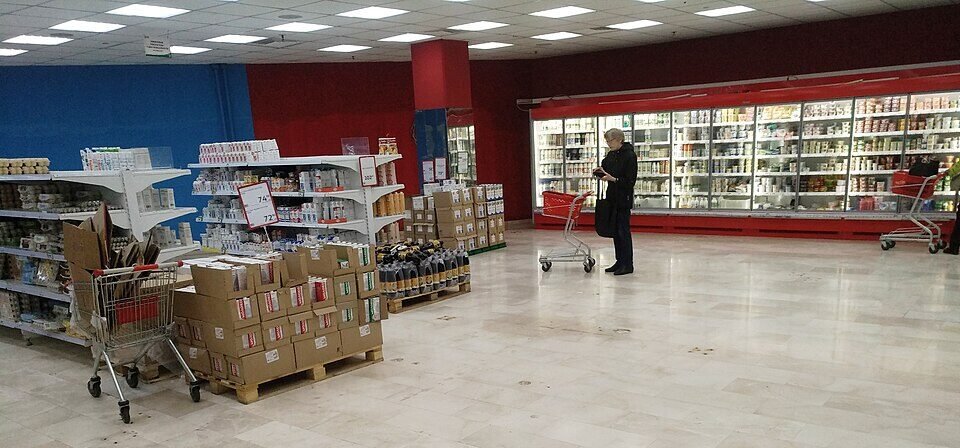
Among the hardest-hit locations were stores in Belgium, where dozens of supermarkets experienced refrigeration failures. At one Delhaize supermarket near Brussels, management estimated losses of around €100,000 after food products had to be discarded due to unsafe storage temperatures.
Items affected reportedly included frozen meals, ice cream, meat products, and other temperature-sensitive goods. Once cooling systems stopped maintaining required temperatures, food safety standards required retailers to remove affected stock from sale.
Store managers described the impact as both costly and disruptive, particularly as businesses worked to replace inventory and minimize interruptions for customers.
While food shelves were replenished as quickly as possible, some locations experienced temporary shortages of frozen and refrigerated items as replacement products were sourced.
How the Attack Allegedly Worked
According to preliminary findings cited by investigators and industry experts, attackers may have gained remote access to temperature-monitoring and control systems used in commercial refrigeration units.
Instead of deploying traditional ransomware or demanding payment, the individuals behind the attacks allegedly manipulated refrigeration settings. Reports indicate that some units were forced into defrost mode, causing internal temperatures to rise dramatically.
In certain cases, temperatures reportedly reached levels far above standard operating ranges, rendering stored food unusable. The unusual nature of the attack has puzzled cybersecurity professionals, who note that the incident appears designed to cause disruption and financial losses rather than generate direct financial gain.
Authorities have not publicly identified any suspects, and no group has claimed responsibility for the incidents.
Growing Concerns Over Connected Devices
The attacks have renewed attention on the cybersecurity risks associated with Internet of Things (IoT) devices. Across Europe and around the world, businesses increasingly rely on connected systems to monitor equipment remotely, improve efficiency, and reduce operating costs.
In supermarkets, centralized management platforms often allow operators to monitor temperatures across hundreds or even thousands of refrigeration units from a single control center. While such systems provide convenience and operational benefits, they also create potential entry points for cyber intrusions if security measures are inadequate.
Industry specialists note that refrigeration units, environmental controls, and other operational technologies have become an important part of modern retail infrastructure. However, these systems do not always receive the same level of cybersecurity attention as corporate servers, laptops, or financial networks.
As a result, vulnerabilities can remain unaddressed for extended periods, providing opportunities for malicious actors.
Existing Security Warnings
Cybersecurity researchers noted that concerns regarding commercial refrigeration security are not entirely new. Similar incidents were reported previously, particularly in France, prompting warnings about potential weaknesses in connected cooling systems.
Experts say software updates and security patches addressing some known vulnerabilities have been available for an extended period. However, implementing updates across large networks of specialized equipment can be a slow and challenging process.
Unlike traditional office technology, commercial refrigeration equipment often remains in service for many years and may be managed by third-party contractors or maintenance providers. Keeping hundreds of devices updated across multiple locations can place significant demands on already stretched IT teams.
This challenge becomes even greater when businesses operate stores across several countries with different suppliers, maintenance schedules, and technical standards.
Investigations Underway
Authorities in the affected countries have launched investigations to determine how the attacks occurred and whether the incidents are linked. Cybersecurity agencies are also working with retailers and technology providers to identify common vulnerabilities that may have been exploited.
At present, investigators have not publicly disclosed specific details regarding the methods used by the attackers. Officials are expected to examine access logs, software configurations, and network activity as part of their inquiries.
The international nature of the incidents suggests that cooperation between national authorities may play a key role in identifying those responsible.
Wider Implications for Retail Security
Beyond the immediate financial losses, the attacks have intensified discussions about the security of connected infrastructure across multiple industries.
Cybersecurity experts warn that attacks targeting physical systems can have consequences far beyond data theft. When connected devices control real-world operations such as refrigeration, transportation, manufacturing, or energy infrastructure, cyber incidents can directly impact business continuity and public services.
The supermarket attacks serve as another reminder that digital threats increasingly affect physical assets as well as information systems.
Many retailers are now reviewing security measures around connected equipment and evaluating whether additional safeguards are required. Some experts have recommended temporarily disconnecting vulnerable systems from the internet until security updates can be verified and implemented.
For now, affected supermarket chains are focused on restoring normal operations, replacing lost inventory, and strengthening cybersecurity defenses. Meanwhile, investigators continue to search for answers as Europe confronts one of the most unusual cyber incidents to affect the retail sector in recent years.BRUSSELS — A suspected cyber attack targeting commercial refrigeration systems has disrupted supermarket operations across at least seven European countries, forcing retailers to dispose of large quantities of spoiled food and raising fresh concerns about vulnerabilities in internet-connected infrastructure.
The incidents, which reportedly affected supermarkets in Belgium, Luxembourg, Sweden, Ireland, Estonia, the Netherlands, and France, have drawn the attention of cybersecurity specialists and law enforcement agencies as they investigate how attackers gained access to refrigeration controls.
Retail operators say the disruptions resulted in significant financial losses, with refrigerated and frozen goods becoming unusable after cooling systems malfunctioned. The attacks have also highlighted the growing risks associated with the increasing use of connected devices throughout the retail sector.
Supermarkets Report Significant Losses
Among the hardest-hit locations were stores in Belgium, where dozens of supermarkets experienced refrigeration failures. At one Delhaize supermarket near Brussels, management estimated losses of around €100,000 after food products had to be discarded due to unsafe storage temperatures.
Items affected reportedly included frozen meals, ice cream, meat products, and other temperature-sensitive goods. Once cooling systems stopped maintaining required temperatures, food safety standards required retailers to remove affected stock from sale.
Store managers described the impact as both costly and disruptive, particularly as businesses worked to replace inventory and minimize interruptions for customers.
While food shelves were replenished as quickly as possible, some locations experienced temporary shortages of frozen and refrigerated items as replacement products were sourced.
How the Attack Allegedly Worked
According to preliminary findings cited by investigators and industry experts, attackers may have gained remote access to temperature-monitoring and control systems used in commercial refrigeration units.
Instead of deploying traditional ransomware or demanding payment, the individuals behind the attacks allegedly manipulated refrigeration settings. Reports indicate that some units were forced into defrost mode, causing internal temperatures to rise dramatically.
In certain cases, temperatures reportedly reached levels far above standard operating ranges, rendering stored food unusable. The unusual nature of the attack has puzzled cybersecurity professionals, who note that the incident appears designed to cause disruption and financial losses rather than generate direct financial gain.
Authorities have not publicly identified any suspects, and no group has claimed responsibility for the incidents.
Growing Concerns Over Connected Devices
The attacks have renewed attention on the cybersecurity risks associated with Internet of Things (IoT) devices. Across Europe and around the world, businesses increasingly rely on connected systems to monitor equipment remotely, improve efficiency, and reduce operating costs.
In supermarkets, centralized management platforms often allow operators to monitor temperatures across hundreds or even thousands of refrigeration units from a single control center. While such systems provide convenience and operational benefits, they also create potential entry points for cyber intrusions if security measures are inadequate.
Industry specialists note that refrigeration units, environmental controls, and other operational technologies have become an important part of modern retail infrastructure. However, these systems do not always receive the same level of cybersecurity attention as corporate servers, laptops, or financial networks.
As a result, vulnerabilities can remain unaddressed for extended periods, providing opportunities for malicious actors.
Existing Security Warnings
Cybersecurity researchers noted that concerns regarding commercial refrigeration security are not entirely new. Similar incidents were reported previously, particularly in France, prompting warnings about potential weaknesses in connected cooling systems.
Experts say software updates and security patches addressing some known vulnerabilities have been available for an extended period. However, implementing updates across large networks of specialized equipment can be a slow and challenging process.
Unlike traditional office technology, commercial refrigeration equipment often remains in service for many years and may be managed by third-party contractors or maintenance providers. Keeping hundreds of devices updated across multiple locations can place significant demands on already stretched IT teams.
This challenge becomes even greater when businesses operate stores across several countries with different suppliers, maintenance schedules, and technical standards.
Investigations Underway
Authorities in the affected countries have launched investigations to determine how the attacks occurred and whether the incidents are linked. Cybersecurity agencies are also working with retailers and technology providers to identify common vulnerabilities that may have been exploited.
At present, investigators have not publicly disclosed specific details regarding the methods used by the attackers. Officials are expected to examine access logs, software configurations, and network activity as part of their inquiries.
The international nature of the incidents suggests that cooperation between national authorities may play a key role in identifying those responsible.
Wider Implications for Retail Security
Beyond the immediate financial losses, the attacks have intensified discussions about the security of connected infrastructure across multiple industries.
Cybersecurity experts warn that attacks targeting physical systems can have consequences far beyond data theft. When connected devices control real-world operations such as refrigeration, transportation, manufacturing, or energy infrastructure, cyber incidents can directly impact business continuity and public services.
The supermarket attacks serve as another reminder that digital threats increasingly affect physical assets as well as information systems.
Many retailers are now reviewing security measures around connected equipment and evaluating whether additional safeguards are required. Some experts have recommended temporarily disconnecting vulnerable systems from the internet until security updates can be verified and implemented.
For now, affected supermarket chains are focused on restoring normal operations, replacing lost inventory, and strengthening cybersecurity defenses. Meanwhile, investigators continue to search for answers as Europe confronts one of the most unusual cyber incidents to affect the retail sector in recent years.

One thought on “Cyber Attack Disables Commercial Freezers Across Seven European Countries, Causing Major Food Losses”